 ISO/IEC 27001 Certification
ISO 27001:2022 certification for your information security management system (ISMS) to protect the confidentiality, integrity and availability of data.
Learn moreEnterprise customers, foreign partners and regulators increasingly require evidence of information security, personal data protection and service continuity. TÜV NORD Vietnam provides certification for these management systems.
ISO/IEC 27001 is the standard most often requested when software companies, BPO providers or data centres bid for or work with international customers. Since its 2025 edition, ISO/IEC 27701 is a standalone privacy information management system (PIMS) standard. With Vietnam’s Law on Personal Data Protection No. 91/2025/QH15 in force since 1 January 2026, ISO/IEC 27701 certification can help demonstrate how an organisation manages personal data.
The transition period for ISO/IEC 27001:2022 ended on 31 October 2025, so valid ISO/IEC 27001 certificates now refer to the 2022 edition, including its updated Annex A controls such as threat intelligence, cloud services security and secure coding.
ISO/IEC 20000-1 is for IT service providers and helps demonstrate that service management processes are controlled in line with service level agreements. ISO 22301 focuses on the ability to maintain and restore operations after a disruption, a common concern in banking, insurance, payments and cloud services.
For outsourcing providers, these certificates can reduce the number of individual customer audits and answer recurring questions in vendor due diligence questionnaires.
These standards and ISO 9001 share a common structure and can be audited together, reducing audit time and sharing processes such as risk assessment, internal audit and management review.
Certification and audit services of TÜV NORD Vietnam that organisations in this sector often choose.
ISO/IEC 27001 Certification ISO 27001:2022 certification for your information security management system (ISMS) to protect the confidentiality, integrity and availability of data.
Learn more ISO/IEC 27701 Certification
ISO 27701:2025 certification for your privacy information management system (PIMS), helping controllers and processors evidence personal data protection.
Learn more ISO/IEC 20000-1 Certification
ISO 20000-1 certification for your IT service management system (SMS) helps IT service providers demonstrate service quality, reliability and control.
Learn more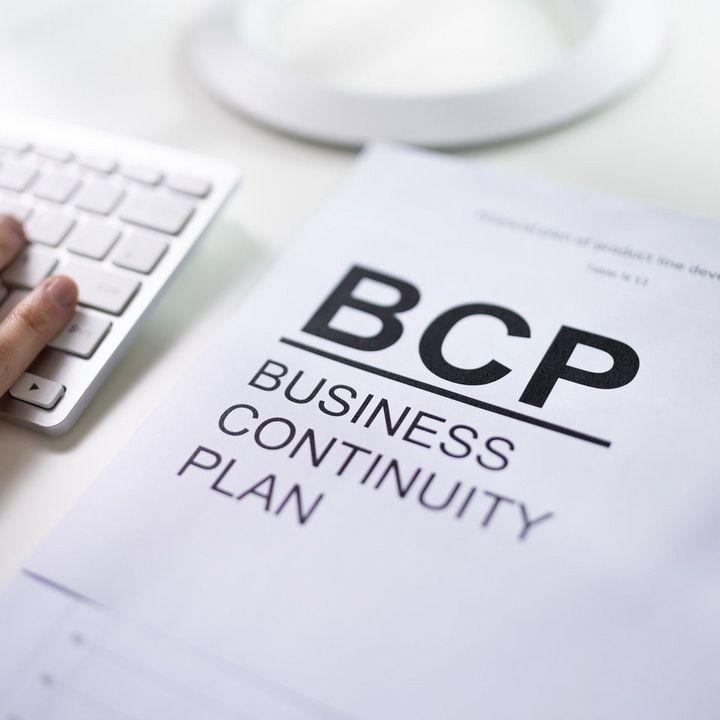 ISO 22301 Certification
ISO 22301:2019 certification for your business continuity management system (BCMS), confirming that your ability to continue and recover is managed.
Learn more ISO 9001 Certification
ISO 9001 certification gives independent evidence that your quality management system meets the standard, now ISO 9001:2026. See how the audit works.
Learn moreContact TÜV NORD Vietnam for detailed information on the certification and audit services relevant to your industry.
Contact usCookies on this website